This is an upstream technical reference retained from the pinned documentation revision. Its diagrams, timings and implementation details are not measurements or release guarantees for Sydekyks. Validate differences against the selected fork release before using it operationally.
How It Works
 When
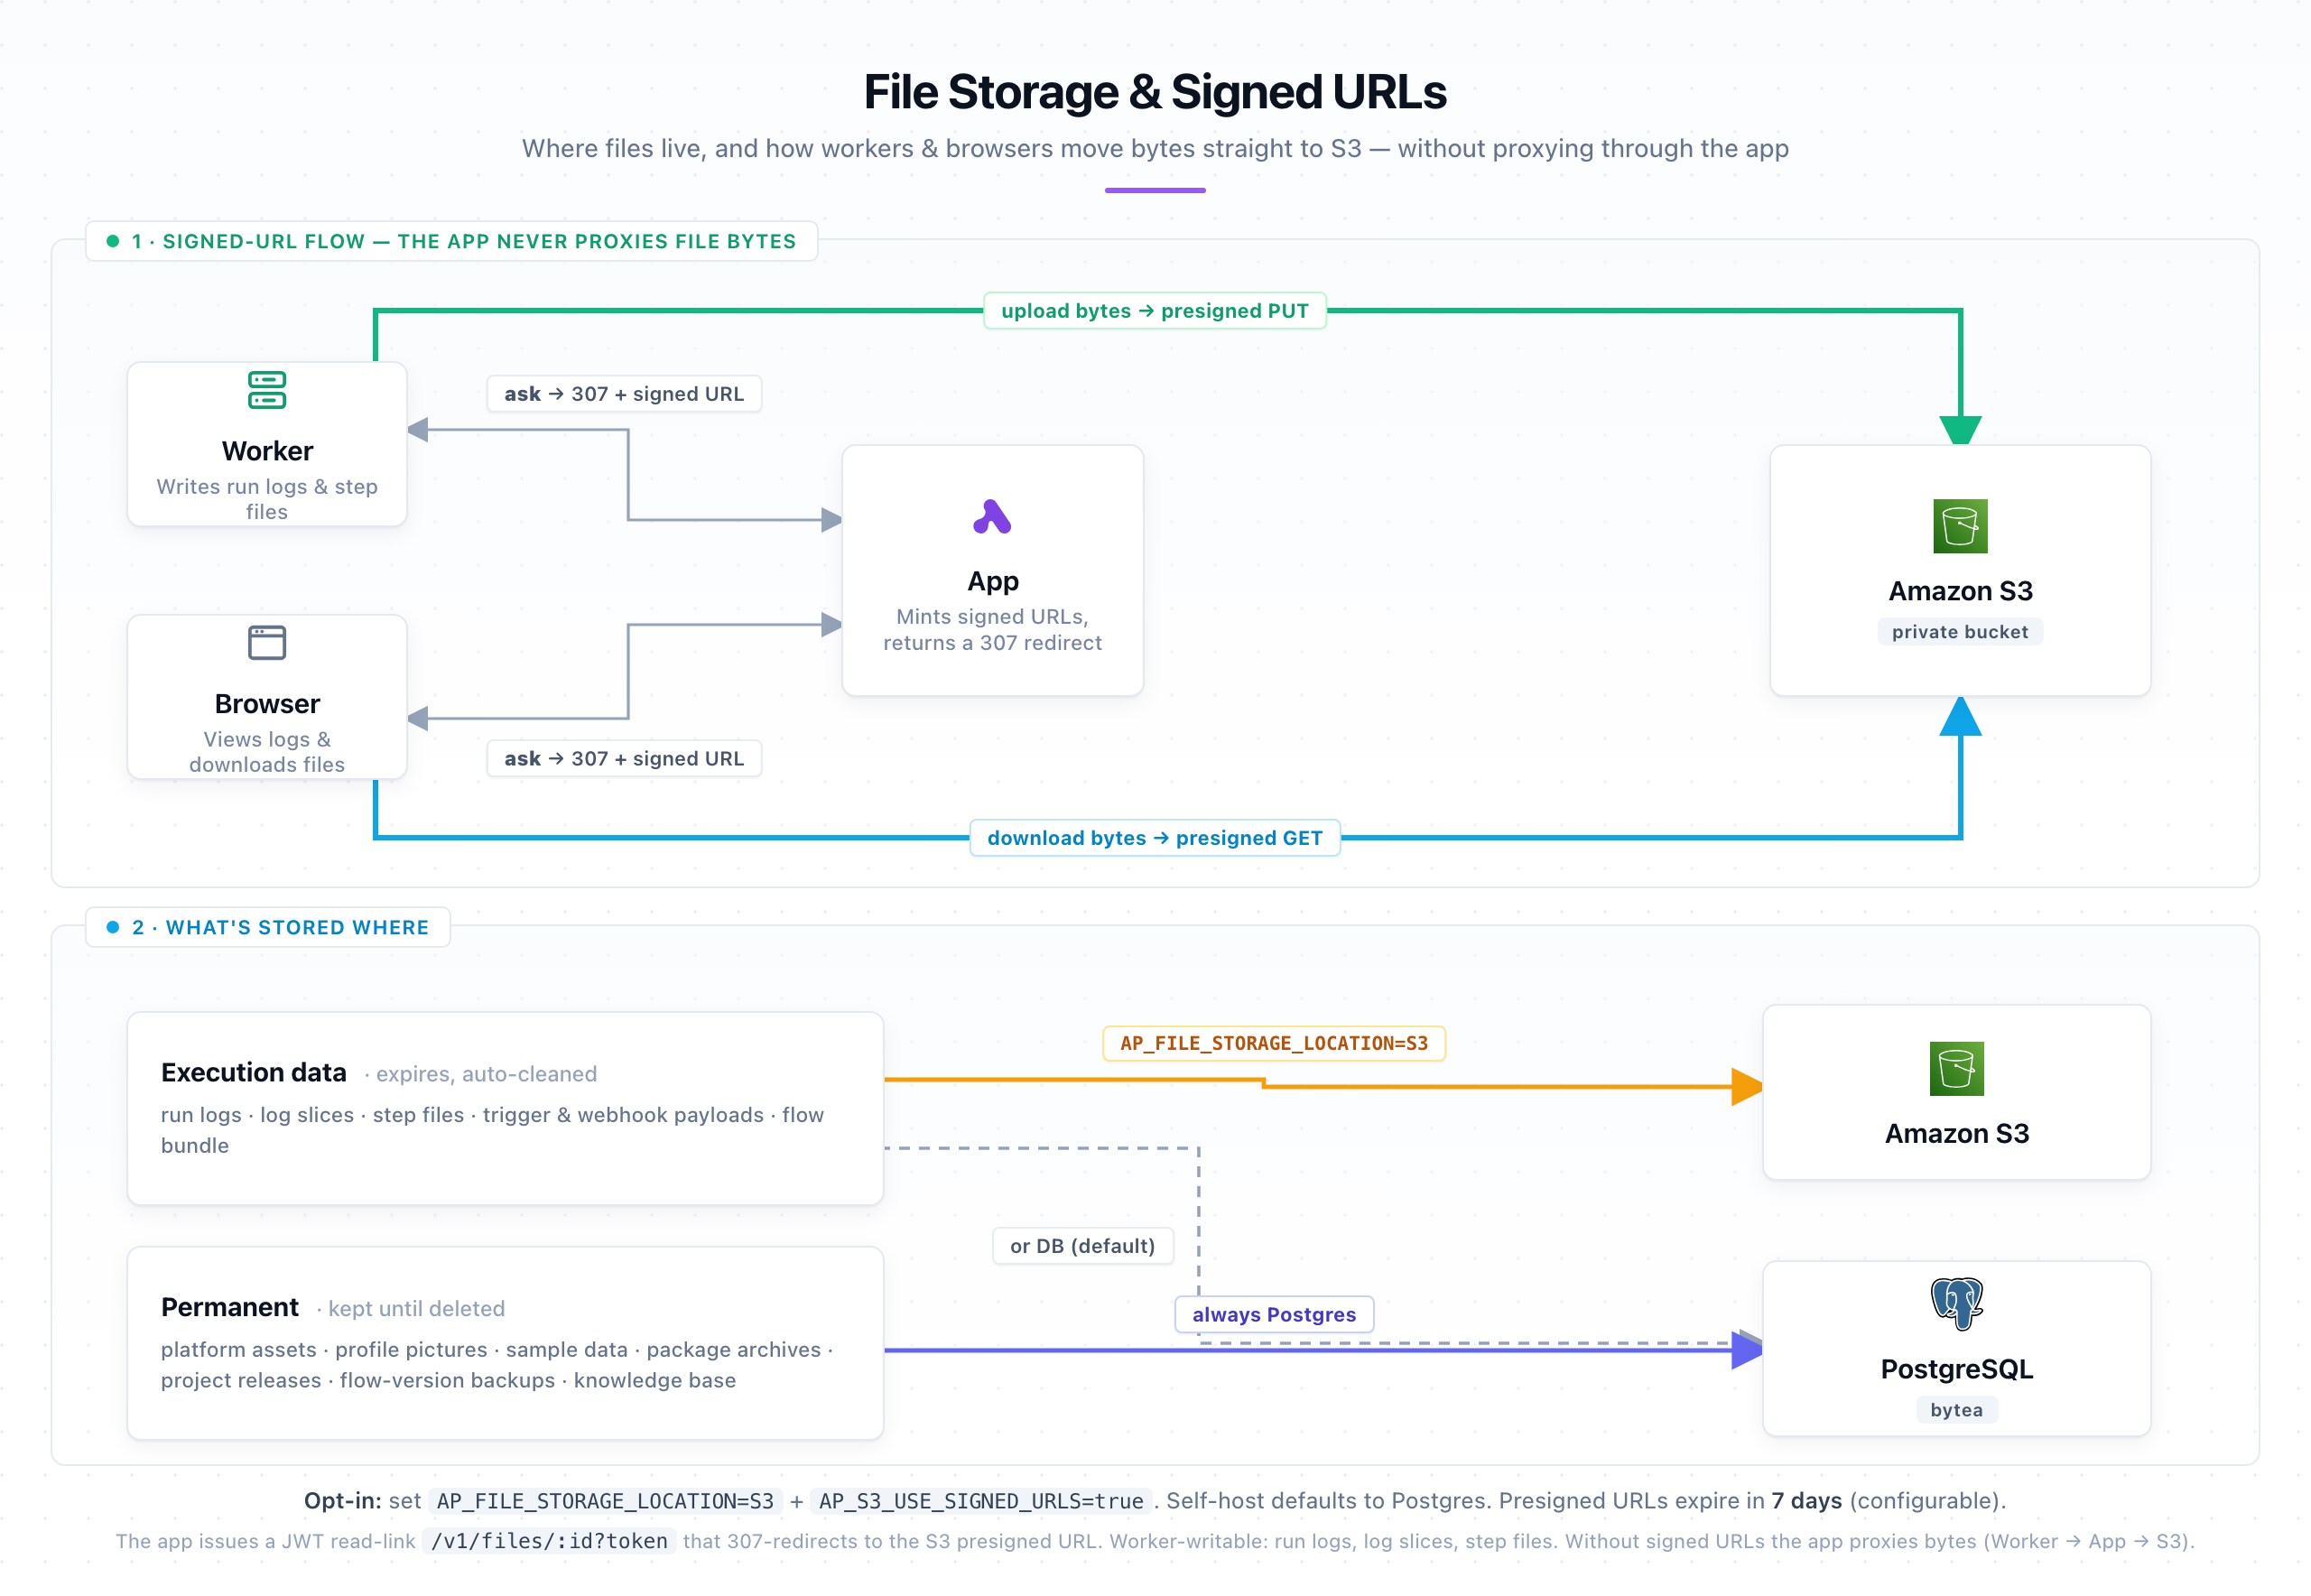
AP_S3_USE_SIGNED_URLS is enabled, the app never proxies file bytes. It mints a short-lived pre-signed URL and returns a 307 redirect, so the worker uploads (and the browser downloads) directly to S3. This keeps heavy file traffic off the API server. Without signed URLs, the app streams the bytes itself (worker → app → S3).
Files split into two groups:
- Execution data (run logs, step files, trigger & webhook payloads, flow bundle) - expires and is auto-cleaned. Its location follows
AP_FILE_STORAGE_LOCATION(S3orDB). - Permanent files (platform assets, profile pictures, sample data, package archives, project releases, flow-version backups, knowledge base) - always stored in Postgres.
Environment Variables
Google Cloud Storage (S3 Interoperability)
Google Cloud Storage works through its S3-interoperability endpoint: setAP_S3_ENDPOINT to https://storage.googleapis.com and use HMAC keys as the access key ID and secret.
The AWS SDK (>= 3.729) defaults to CRC32 checksums and aws-chunked payloads on PutObject, which GCS’s S3-interop endpoint rejects with SignatureDoesNotMatch. Set these two environment variables on the app and worker containers to restore the old behavior: